Apple Begins Scanning Public iCloud Links for ‘Harmful Content’ in iOS 27.3
Toggle Dark Mode
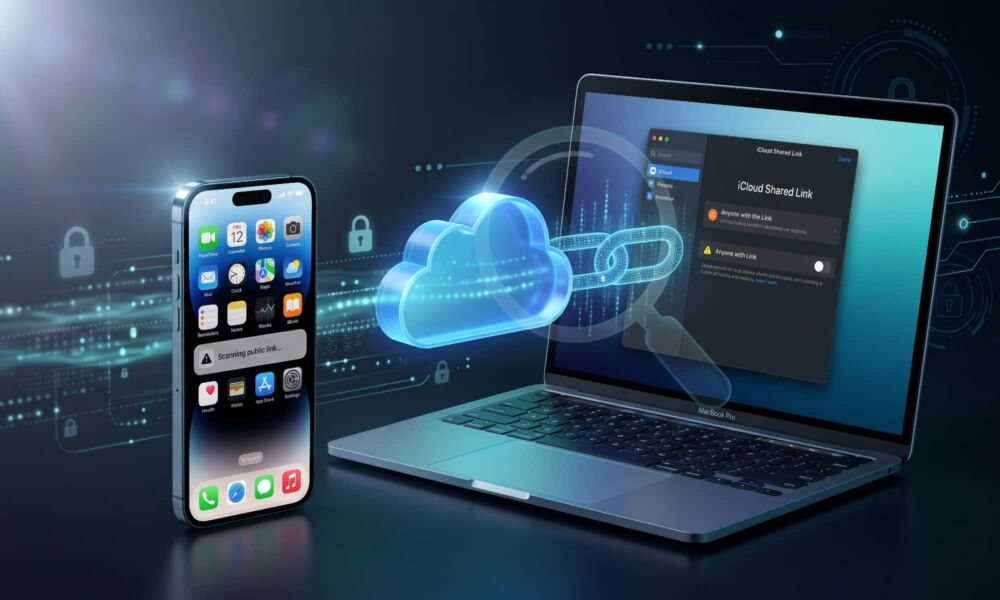
It turns out that iOS 27.3 and the gang are bringing a more subtle change behind the scenes, with Apple quietly announcing that it will begin checking items publicly shared from iCloud Drive or iCloud Photos for “harmful content.”
While that may sound a bit privacy invasive on the surface, it’s actually not nearly as controversial as the company’s aborted plan to scan for child sexual abuse materials (CSAM). That well-intentioned initiative would have scanned all photos uploaded to iCloud against a database of known CSAM maintained by the National Center for Missing and Exploited Children (NCMEC).
It was a noble idea, but many privacy advocates pointed to a slippery slope that could open the door to abuse by oppressive states, as the NCMEC baseline database could just as easily be swapped out for things like images of political dissidents or activity by human rights activists. In the end, Apple killed the plan, citing the danger of opening “new threat vectors for data thieves to find and exploit,” and “a slippery slope of unintended consequences.”
Still, the company hasn’t given up on preventing its platform from being used to distribute harmful content, but for now, it’s focusing entirely on items that are shared publicly — photos, files, and iOS 27 Shared Albums made available to “Anyone with the Link” (as opposed to “People you choose”).
Apple outlines this in a new support document that was published yesterday:
When you share an item that can be accessed by Anyone with the Link in version 27.3 or later of iOS, iPadOS, macOS, and visionOS, that content is made accessible to Apple to check for harmful content.
As Apple goes on to explain, such content “is accessible to anyone who has the link, including Apple.” That arguably makes it fair game for Apple to scan these items to ensure that they contain no harmful content. However, there’s another important wrinkle here, as Apple explains:
When you share an item that can be accessed by Anyone with the Link, to facilitate that sharing, the item is no longer end-to-end encrypted, even if the owner or participants have turned on Advanced Data Protection.
The phrasing here suggests that at one point items that were accessible to “Anyone with the Link” were somehow protected using end-to-end encryption. It’s not entirely clear how that worked, considering these shared items can be viewed and downloaded using a standard web browser, but presumably Apple wants to make this absolutely clear.
It’s worth noting that items publicly shared from iCloud Drive or iCloud Photos generate a random, obscure link, so they’re realistically only accessible to folks who have the link. However, the moment you give that link to even one person, you’re at the mercy of what they do with it, and all bets are off on limiting the distribution if you post it on social media or even in a group chat.
Either way, those links are generated by Apple in the first place, so it knows what they are and can therefore scan what’s behind them as they’re created. Apple notes that it “reserves the right to move, refuse, modify, remove, or delete the [harmful] content at any time,” and may take action against users who “try to upload harmful content,” including blocking or disabling their Apple Account, barring their email or phone number from creating a new one, or even involving law enforcement.